
CMXfor IT and security
Separation enforced in the database, audit on every change, data stored in your region.
Separation enforced in the database.
Tenant separation enforced in the database and proved by leak tests on every release. Admin roles give no contract access.
Your sign-in.
Sign in with the Microsoft or Google identity your company already has. Your workspace has one sign-in domain, and sessions end when idle and after a set time.
AI kept in bounds.
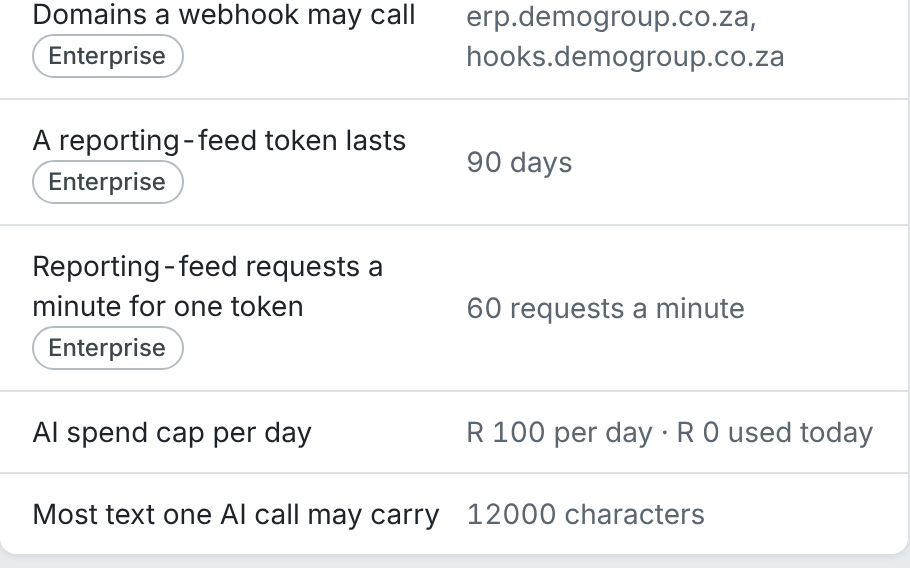
Contract text is data, never instructions. The AI never sees a contract the person asking cannot open. Zero retention and no training on your data, and a daily spend cap you set.
Stored in your region.
Your contracts are stored in your region: South Africa today, with EU and US hosting on request as a dedicated deployment.
Privacy laws.
CMX is built for POPIA and the privacy laws modelled on the same principles: data stored in your region, access decided in the database and limited to the people who need it, an audit trail of every change, retention and deletion you set, signers’ details shown only to people who can open the contract, and a breach procedure.